


What Is a Home Subscriber Server (HSS)?
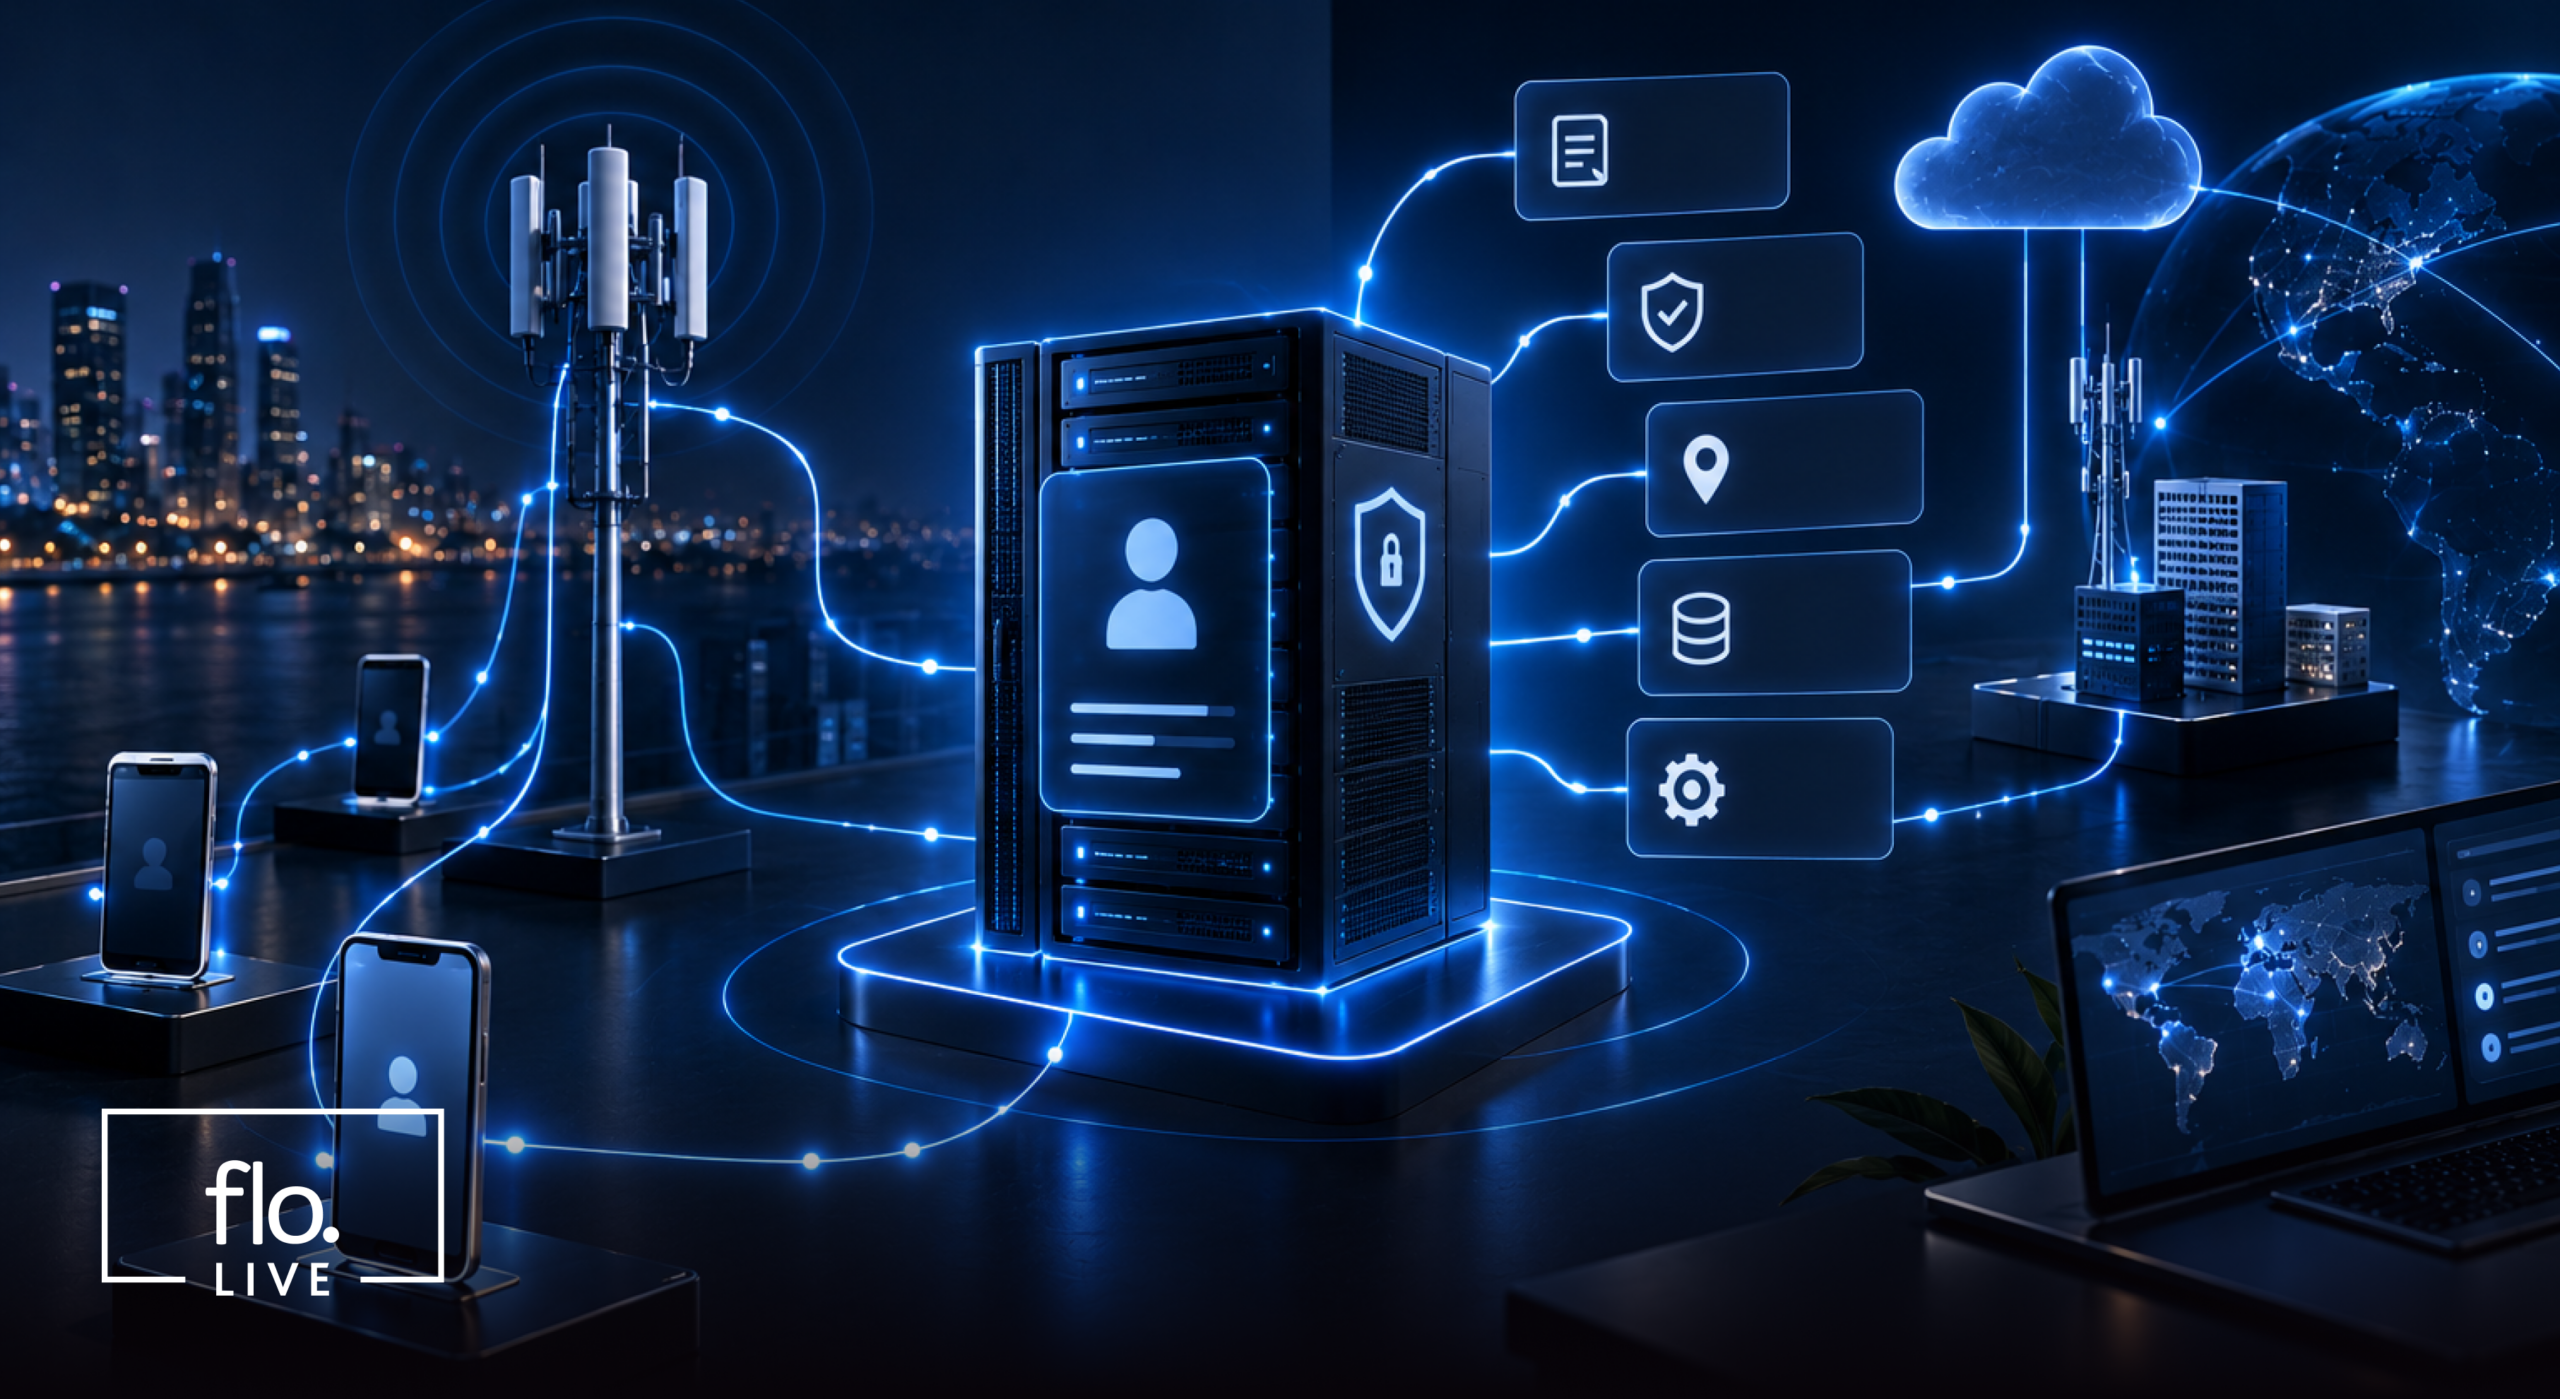
A Home Subscriber Server (HSS) is the master user database in 4G LTE and IP Multimedia Subsystem (IMS) networks. It securely manages subscriber profiles, performs device authentication, and records which network node is currently serving each subscriber.
Functioning as the modern evolution of the older GSM Home Location Register (HLR), the HSS carries out several core responsibilities:
- Subscriber profile management: It retains specific user subscription data, dictating what services, data caps, and roaming privileges a specific user is permitted to use.
- Authentication and authorization: It securely stores subscriber credentials and generates security keys to prevent unauthorized network access.
- Location management: The HSS tracks where a subscriber is registered (e.g., handling mobility between serving nodes like the MME) and helps route calls and data sessions.
- IMS and VoLTE support: Supports IP-based voice, video, messaging, and multimedia services by providing subscriber data and authentication for IMS and VoLTE sessions.
- Interface with other network elements: Communicates with components such as the MME, CSCF, policy servers, and charging systems to exchange subscriber, location, and service information.
In 5G networks, many HSS functions are absorbed by the Unified Data Management (UDM) and Unified Data Repository (UDR) frameworks.
This is part of a series of articles about cellular technologies
Why Is HSS Important in Mobile Networks?
Subscriber Authentication
Subscriber authentication is one of the primary roles of the HSS in a mobile network. When a user attempts to connect, the HSS verifies their identity using stored credentials, such as IMSI (International Mobile Subscriber Identity) and authentication keys. This process protects the network from unauthorized access and fraud, ensuring that only valid subscribers can use network services. The authentication process typically involves challenge-response mechanisms that protect against impersonation and replay attacks.
Service Authorization
After authentication, the HSS determines what network resources and services a subscriber can access. Each subscriber profile in the HSS contains information about subscribed services, permitted network features, and policy rules. When a user initiates a session or requests a service, the HSS checks the profile to authorize or deny access based on subscription details and network policies. This control supports proper billing, compliance with regulatory requirements, and efficient network resource allocation.
Mobility and Session Support
Mobility and session support enable consistent user experiences as subscribers move across network zones or geographic locations. The HSS records which serving node (the MME in LTE, or the SGSN in legacy packet networks) is currently handling each subscriber. That registration is what allows incoming calls, messages, and sessions to be routed to the right part of the network. It is updated when a subscriber moves to a different serving node, not every time a device changes cell: cell and tracking-area level location is maintained by the MME. The HSS plays a central role in session management by coordinating with these elements.
Centralized Subscriber Data Management
Centralized subscriber data management is a core function of the HSS. By consolidating subscriber-related information into a single database, the HSS reduces data silos and duplication. This approach simplifies operations, improves data consistency, and supports provisioning, updates, and policy enforcement across the network. Operators can manage millions of subscriber profiles while maintaining accurate and current information.
Key Functions of a Home Subscriber Server
1. Subscriber Profile Management
The HSS maintains subscriber profiles that include personal identification, service subscriptions, access permissions, and policy rules. These profiles determine how each subscriber interacts with the network, what services they can use, and under what conditions. When a user connects or requests a service, the HSS provides the relevant profile information to other network elements, supporting consistent and policy-compliant service delivery.
Profile management allows operators to update, modify, or deactivate subscriber information as needed. This supports:
- Onboarding new users
- Adjusting service plans
- Responding to lost or stolen devices
By maintaining a centralized repository of subscriber data, the HSS simplifies network management and supports the subscriber experience.
2. Authentication and Authorization
Authentication and authorization are closely linked but distinct functions of the HSS. Authentication verifies a subscriber’s identity using credentials such as SIM-based keys and cryptographic algorithms. This step is required before granting access to network resources and protects against unauthorized use and network breaches. The HSS handles authentication in coordination with other security components.
Once a subscriber is authenticated, the HSS determines the services and access levels available based on the subscriber’s profile and network policies. This authorization process allows operators to:
- Enforce differentiated service levels
- Apply policy changes
- Meet regulatory requirements
By managing authentication and authorization centrally, the HSS supports secure and controlled service delivery.
3. Location Management
Location management, in HSS terms, means keeping an accurate record of which node is serving each subscriber. The MME or SGSN informs the HSS of its identity through the Update Location procedure whenever it takes over service for a device, on initial attach, and again when a subscriber moves to a different serving node or roams onto another network. The HSS uses that registration to route incoming voice calls, SMS, and data sessions to the correct serving node, and cancels the previous registration when service moves.
Accurate serving-node registration also underpins:
- Location-based billing
- Correct routing of terminating calls and messages
- Roaming control, including operator-determined barring and roaming restrictions
By maintaining a real-time view of subscriber locations, the HSS helps allocate resources and manage service delivery for mobile users.
4. IMS and VoLTE Support
The HSS supports IP Multimedia Subsystem (IMS) and Voice over LTE (VoLTE) services. In IMS architectures, the HSS stores subscriber profiles, authentication data, and service entitlements for IP-based communications. It interacts with IMS core components, such as the Call Session Control Function (CSCF), to authenticate users and authorize access to multimedia services like voice, video, and messaging over IP networks.
For VoLTE, the HSS ensures that authenticated and authorized subscribers can initiate and receive voice calls over LTE. It provides subscriber context, policy information, and session parameters to the IMS core, enabling:
- Call setup
- Call handover
- Termination
5. Interface with Other Core Network Elements
The HSS interfaces with multiple core network elements to support authentication, authorization, mobility, and service delivery. Key interfaces include the S6a interface with the MME in LTE networks, the Cx and Sh interfaces with IMS components, and other Diameter-based interfaces for policy and charging functions. These interfaces enable real-time exchange of subscriber information, location updates, and policy data.
By maintaining standardized interfaces, the HSS supports interoperability and coordination with other network functions, such as:
- Policy control
- Charging
- Service delivery platforms
This integration supports roaming, interworking with legacy systems, and the introduction of new services.
HSS vs HLR: What’s the Difference?
The Home Subscriber Server (HSS) and the Home Location Register (HLR) both serve as subscriber databases, but they are built for different network generations and have distinct roles. The HLR is the primary subscriber database for 2G and 3G networks, managing subscriber information, authentication data, and location tracking. The HSS is used in 4G LTE and IMS networks, supporting IP-based services and integration with modern authentication and policy management systems.
The HSS extends the capabilities of the HLR by supporting richer subscriber profiles, mobility management, and integration with IMS and next-generation network services. It uses signaling protocols such as Diameter, while the HLR relies on legacy protocols such as MAP (Mobile Application Part). The shift from HLR to HSS reflects the move toward all-IP architectures and more flexible service provisioning.
Common HSS Interfaces and Protocols
Diameter Protocol
The Diameter protocol is the primary signaling protocol used by the HSS to communicate with other core network elements in LTE and IMS networks. It was developed as the successor to RADIUS and provides authentication, authorization, and accounting (AAA) capabilities for IP-based networks. Diameter enables exchange of subscriber information, policy data, location updates, and session-related messages between the HSS and network functions such as the MME, Policy and Charging Rules Function (PCRF), and IMS components.
Usage:
Diameter supports application-specific interfaces through dedicated Diameter applications, allowing different network functions to exchange specialized information within a common signaling framework. It also includes mechanisms for failover, peer discovery, and secure transport.
S6a Interface
The S6a interface connects the HSS to the Mobility Management Entity (MME) in LTE networks. It supports subscriber authentication, authorization, location management, and mobility procedures. When a device attaches to the LTE network, the MME communicates with the HSS over the S6a interface to retrieve subscriber data and obtain authentication vectors to verify the user’s identity.
Usage:
The S6a interface allows the HSS to provide subscription information, roaming permissions, and service restrictions to the MME. When a subscriber attaches to a different MME (on relocation or when roaming onto another network) the new MME registers itself with the HSS, which then cancels the registration held by the previous MME. Tracking-area changes within one MME are handled locally and do not involve the HSS. This exchange ensures that calls, messages, and data sessions are routed correctly.
Cx Interface
The Cx interface is used between the HSS and Call Session Control Function (CSCF) components within the IMS architecture. Its primary purpose is to support user registration, authentication, and service authorization for IP-based multimedia services. When a subscriber registers with the IMS network, the CSCF queries the HSS over the Cx interface to obtain authentication data and determine which services the user can access.
Usage:
The Cx interface allows the HSS to provide routing information and subscriber service profiles to IMS components. This information helps the IMS core route calls and deliver services such as VoLTE, video calling, and messaging.
Sh Interface
The Sh interface allows application servers within the IMS environment to access subscriber-related information stored in the HSS. Unlike the Cx interface, which is used for registration and session control, the Sh interface focuses on retrieving and updating subscriber profile data for value-added services and applications.
Usage:
Through the Sh interface, application servers can obtain information such as user preferences, service settings, presence data, and service-specific profiles. By centralizing subscriber data and allowing controlled access through standardized interfaces, the HSS supports consistent service behavior and simplified management across the IMS ecosystem.
Home Subscriber Server Use Cases
Mobile Network Operators
Mobile Network Operators (MNOs) are the primary users of HSS platforms in LTE and IMS networks. The HSS serves as the central repository for subscriber identities, authentication credentials, service subscriptions, and mobility information. It supports operations such as subscriber provisioning, network access control, roaming management, and policy enforcement across large subscriber bases.
For operators, the HSS supports consistent services across voice, messaging, and data networks. It enables management of subscriber information while supporting large-scale authentication and mobility procedures. By centralizing subscriber data, operators can simplify network administration and introduce new services.
MVNOs
Mobile Virtual Network Operators (MVNOs) use HSS platforms to manage subscriber information and service entitlements while relying on host network operators for radio access infrastructure. Depending on the MVNO model, the HSS may be owned by the MVNO or shared with the host operator. In either case, it provides a centralized system for managing subscriber profiles, authentication data, and service policies.
The HSS allows MVNOs to control customer services and differentiate their offerings without building a complete mobile network. It supports subscriber onboarding, plan management, roaming control, and service customization.
VoLTE and IMS Providers
VoLTE and IMS providers rely on the HSS to authenticate users and manage service profiles for IP-based communication services. The HSS stores the subscriber information required for IMS registration, call routing, and service authorization. When a user initiates a VoLTE call or accesses multimedia services, IMS components query the HSS to verify permissions and retrieve service settings.
The HSS supports consistent user experiences across multimedia applications such as:
- Voice
- Video
- Messaging
By supplying subscriber profiles and authentication data to the IMS core, it supports session continuity and feature management.
Private LTE / 5G Networks
Private LTE and 5G networks use HSS platforms to manage access for employees, devices, sensors, and industrial equipment. In these environments, the HSS acts as the central subscriber database, controlling authentication, authorization, and mobility for connected endpoints. Organizations can define access policies and service permissions based on operational requirements.
Common deployments include:
- Manufacturing facilities
- Ports
- Utilities
- Transportation systems
- Enterprise campuses
The HSS ensures that authorized users and devices can access the network while supporting secure communications and mobility across the coverage area.
HSS Best Practices for Global IoT Connectivity
Here are some important practices to consider when using the Home Subscriber Server for IoT connectivity.
1. Centralize Subscriber Data But Localize Network Access
For global IoT deployments, maintaining a centralized HSS provides a single source of truth for subscriber profiles, authentication credentials, policies, and device status. Centralized management supports provisioning, troubleshooting, compliance reporting, and operational oversight across multiple countries and network partners. It also ensures consistent policy enforcement regardless of device location.
At the same time, network access should be localized when possible. Local connectivity can reduce latency, support regulatory requirements, and reduce roaming dependencies. By combining centralized subscriber management with localized network access, organizations can support operational efficiency and device performance globally.
Key actions:
- Maintain a centralized HSS for subscriber profiles, policies, and authentication data.
- Use local network breakouts and regional connectivity where regulatory requirements apply.
- Synchronize subscriber updates across global and regional network environments.
Related content: Understand how Access Point Names (APNs) control IoT network access.
2. Prioritize Security for Subscriber Identity and Authentication Data
The HSS stores sensitive information in a mobile network, including subscriber identities, authentication keys, and service entitlements. Protecting this data is critical because a compromise can lead to unauthorized network access and service fraud. Strong access controls, encryption, network segmentation, and continuous monitoring should protect HSS infrastructure and subscriber records.
Operators should adopt key management practices and regularly audit authentication processes. Security measures must extend beyond the HSS to connected systems, interfaces, and provisioning platforms. A layered security approach protects subscriber information and overall network integrity.
Key actions:
- Encrypt subscriber data at rest and in transit.
- Implement strict role-based access controls for HSS administration.
- Monitor HSS interfaces and authentication activity for suspicious behavior.
3. Use Real-Time Provisioning and Lifecycle Management
IoT deployments often involve large numbers of devices that may be activated, suspended, modified, or retired throughout their lifecycle. Real-time provisioning allows subscriber profiles and network permissions to be updated as business requirements change. This reduces operational delays and ensures devices remain connected with the correct service configurations.
Lifecycle management should cover onboarding, activation, policy updates, diagnostics, suspension, reactivation, and decommissioning. Automating these processes through integration with the HSS reduces manual errors. Real-time control is important for IoT applications where device availability and responsiveness affect operations.
Key actions:
- Automate device onboarding and activation workflows.
- Update subscriber profiles and service policies dynamically.
- Implement automated deactivation and retirement processes for unused devices.
4. Support Multi-Network and Multi-IMSI Operations
Global IoT deployments often depend on access to multiple mobile networks to increase coverage and resilience. An HSS architecture that supports multi-network connectivity allows devices to connect to available networks while maintaining a consistent subscriber identity and service profile. This flexibility reduces coverage gaps and improves reliability across regions.
Support for multi-IMSI technologies allows devices to switch between operator profiles when needed. This approach can improve network availability, manage costs, and address regulatory requirements in specific countries. The HSS should manage these subscriber relationships while maintaining authentication and policy enforcement.
Key actions:
- Enable connectivity across multiple carrier networks.
- Support dynamic IMSI switching based on coverage and policy requirements.
- Monitor network performance to optimize carrier selection and availability.
5. Keep HSS Integrated with the Wider Connectivity Platform
The HSS provides more value when it operates as part of a broader connectivity ecosystem rather than as a standalone database. Integration with provisioning systems, SIM management platforms, policy control functions, analytics tools, billing systems, and IoT management platforms enables visibility and automation across the subscriber lifecycle.
An integrated HSS allows organizations to automate workflows, synchronize subscriber information across systems, and respond to operational events. It also provides insight into device behavior, network usage, and service performance. For global IoT deployments, this integration supports scalability and connectivity management.
Key actions:
- Integrate the HSS with SIM management and provisioning systems.
- Connect subscriber data to billing, analytics, and policy control platforms.
- Automate workflows between the HSS and IoT device management solutions.
How FLOLIVE® Manages Subscriber Data and Authentication for Global IoT Connectivity
FLOLIVE® delivers global IoT connectivity through a cloud-native, globally distributed core network with local points of presence worldwide. Rather than depending on traditional, high-latency roaming, Flolive’s “Global-Local” approach lets every device connect to a local core in its region while subscriber identities, authentication, and policies are managed centrally. This brings the subscriber-data and authentication roles of the HSS together with localized network access, giving enterprises one localized global network that keeps every device connected and compliant across 750+ networks and 15+ carrier partners.
Key capabilities of Flolive Global IoT Connectivity:
- Localized global core network: Flolive’s cloud-managed network applies local profiles and enables local breakout across continents, reducing latency and keeping data within national borders.
- Centralized connectivity management: The Connectivity Management Platform (CMP) provides single-pane-of-glass visibility, letting you monitor data usage, manage security policies, and switch network profiles for every global device from one dashboard.
- Multi-IMSI authentication and identity switching: A patented Multi-IMSI over eUICC platform automatically provisions a native local identity when a device enters a restricted market, ensuring permanent-roaming-safe, compliant connectivity.
- Support for any SIM form factor: The platform supports plastic SIMs, embedded MFF2 eSIMs, iSIM, and softSIM, with seamless activation, smart switching, and full lifecycle control across all devices and geographies.
- Any cellular technology from 2G to 5G and satellite NTN: Globally distributed core networks support all cellular technologies, including LPWA and satellite Non-terrestrial Networks, under a single unified platform.
- Data sovereignty and compliance: Localized connectivity helps companies adhere to data privacy laws such as GDPR and CCPA by ensuring data does not leave the country it originated in.
Learn more about how Flolive keeps every device connected, authenticated, and compliant with its Global IoT Connectivity solution.